Leif Ames

MapQuest creates a new layer (that can be toggled on and off), Gizmodo reports: After promising not to comply with the Trump administration's "Lake America" gimmick, the platform announced a new "Surveillance Layer" that displays the locations of automated license plate readers (ALPRs), including those from Flock Safety. Per MapQuest, its new tool will identify the locations of known outdoor surveillance cameras and plate readers from Motorola Solutions (Vigilant), Genetec, Axis Communications, Axon, Leonardo (ELSAG), Neology, Rekor, PlateSmart, Ubicquia, Verkada, and others. While the company didn't specify how it sources its data, it appears to be similar to the data amassed by DeFlock, which maintains a user-submitted map of ALPR camera locations. MapQuest may be sourcing the information from DeFlock and the OpenStreetMap project. Engadget notes that MapQuest also recently added "useful, long-overdue features like Android Auto support and public transit directions."

Read more of this story at Slashdot.

"Jeff Bezos' Blue Origin said Friday it plans to make extensive upgrades to its Florida launch facilities," reports CNBC, "with the goal of supporting multiple flights per week by the end of the decade." "The company will add two more launch and landing pads for New Glenn, its heavy-lift, partially reusable rocket." A $330 million expansion to its Rocket Park campus in Cape Canaveral, expected to be complete in the summer of 2027, will enable it to produce up to 150 upper stages of its New Glenn rocket annually, Blue Origin said in a blog post. "These investments are centered on one goal: building the capacity to support more missions, more reliably, and more efficiently," Ian Richardson, Blue Origin's senior vice president of operations, wrote in the post. "As we look ahead, this infrastructure is designed to support multiple flights per week by the end of the decade...." Blue Origin said it's building a new customer integration facility with the U.S. Space Force at Cape Canaveral Space Force Station that will enable it to "prepare multiple missions at once" when it's up and running. Blue Origin has invested more than $3 billion in its infrastructure and facilities in Florida, which now spans more than 20 sites across the state's Brevard and Orange counties, with more than 5,000 employees, [Ian Richardson, Blue Origin's senior vice president of operations, wrote in the blog post]. The article notes it's part of "a flurry of investment" as SpaceX stops offering commercial rides on its Falcon 9, "with $92.5 billion invested in the commercial space sector in the first three quarters of 2026, according to a report this week by venture capital firm Space Capital." And it happens as Blue Origin, SpaceX and other rocket providers "are seeing increasing demand from companies and governments trying to deploy satellites into orbit." "Launching at a high cadence requires a connected system," says Blue Origin's blog post, "one that manufactures vehicles at scale, prepares customer payloads efficiently, supports reliable launch operations, and quickly returns reusable boosters to service. We are building that system here in Florida," and "laying the foundation for a future where access to space is more frequent, more reliable, and more affordable, for the benefit of Earth."

Read more of this story at Slashdot.

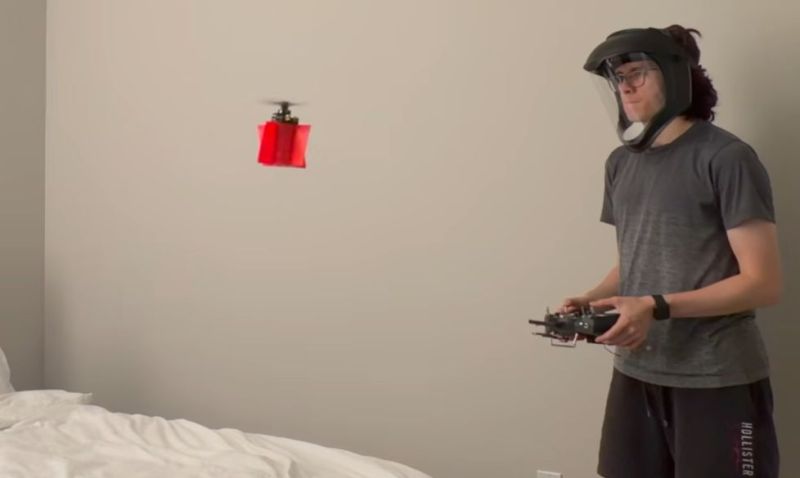
Technically all that you need in order to make a drone fly is a single motor and single propeller, but realistically it becomes basically impossible to fly it at that …read more
family; household / CL:戶|户[hu4] (HSK 2)

Federal officer slammed vehicle into a construction worker while pursuing a man who died in similar circumstances

A federal officer slammed a vehicle into a Houston construction worker and broke his leg, believing him to be a man who apparently died years ago, the dead man’s family said on Friday, further calling into question the account given by US Immigration and Customs Enforcement (ICE).

The worker, 48-year-old Miguel Parra Hernandez of Mexico, remains hospitalized with multiple leg fractures and needs reconstructive ankle surgery, according to FIEL, a Houston-based immigration advocacy group. At a news conference on Friday, the group said the alleged suspect’s family had shared documentation proving his death.

Continue reading...
Linux maintainers "have ruled that people no longer have to declare their LLM usage," reports XDA Developers, "as Torvalds himself calls a ban on AI 'utterly stupid.'" The first part of this story comes via a message sent to the Linux mailing list. It announces one of the major changes decided during the Maintainers Summit on October 8, 2026, in Prague, Czechia, where submissions to the kernel no longer need to use the "Assisted-by" tag... meaning that people can submit AI-generated code without needing to declare it as such. In some correspondence regarding concern about this new disclosure removal, the creator of Linux, Linus Torvalds, made his thoughts known... [Torvalds] compares an AI ban to getting rid of text editors, as doing so would prove that someone could write a good commit message without making any mistakes. He then rounds off his argument by asking, "Do you not see how UTTERLY STUPID those kinds of rules would be?" and stating that he simply expects the people working on the Linux kernel to "understand what they are doing." Here's the last line of Torvalds' post. "Quite honestly, in my experience, the people I respect and call intelligent are not the ones that shy away from using new and interesting tools." In a related story, Torvalds says he's used AI to help him understand patches that were hard to follow. And this week Torvalds even posted an LLM-assisted patch, reports Tom's Hardware: The development branch purports to fix an old issue with massive cache contention when many CPUs are reading the same file — a scenario potentially encountered when using shared libraries, databases, and web servers. Several developers had already made attempts over the years at fixing the issue, all with varied results, none quite ideal as an all-encompassing solution... He's now posted his solution in a development branch, and claims that he's seen a 23x performance improvement in a dedicated synthetic benchmark, though he notes that actual real-world impact will be far less significant, as "no real load" will witness those figures. Torvalds used Anthropic's Claude Code, reports The New Stack, and "said the assistant wrote the implementation, tests, and initial documentation, and reviewed the code under his direction. He ran the benchmarks himself, despite having previously criticized developers for claiming AI writes 99% of their code." Tuesday Torvalds submitted a 10-patch series. "Reviewers have since identified a race condition and raised concerns about memory reclamation," adds The New Stack. "Torvalds has handed further development to Kiryl Shutsemau, a Linux kernel developer who previously worked on the same bottleneck."

Read more of this story at Slashdot.

About 6,000 homes under evacuation, affecting 16,000 residents in San Clemente and San Juan Capistrano

At least six homes burned and two firefighters were injured after a fast-moving wildfire blazed through parts of southern California on Friday.

Two firefighters were taken to the hospital with heat-related injuries from the Norte fire, officials said.

Continue reading...

Prosecution did not act in fair and impartial way in grand jury proceedings, judge rules, after West Wing actor charged with groping young boy on TV set

A state court ⁠judge in New Mexico has dismissed charges of child sexual abuse against West Wing actor and director Timothy Busfield, saying the prosecution did not act in a ⁠fair and impartial manner during grand jury proceedings.

Judge Joseph Montano said prosecutors could pursue new charges against Busfield.

Continue reading...
"Cloudflare has acquired Deno, the company behind the [server-side] JavaScript and TypeScript runtime created by Ryan Dahl, the inventor of Node.js," Forbes reported last week. But Deno "has no future at Cloudflare, which will maintain the runtime for another year before ending its development," writes The Register. "That's OK with Dahl. 'I am now of the opinion that if you're choosing Node.js for building servers, you're doing it wrong,' Dahl told The Register." It all started with his team's work on the platform Deno Deploy, "We wanted to make running applications as straightforward as possible," Dahl wrote on the official Deno blog. "But building and operating Deploy also showed us how much complexity remained underneath that developer experience. I wanted to simplify that layer, too." This led to celld. Building on the Cloudflare Workers programming model, celld lets developers build distributed applications from the start while making the system simple to operate. What excites me greatly is that the scaling is built into the programming model, rather than infrastructure each app has to assemble itself.... We want to make this programming model the default way to build servers, whether you run on Cloudflare's network or your own infrastructure. Joining also means choosing where to focus our effort... Deno will remain open source, and we welcome others who want to continue its development. Deno Deploy will continue operating for six months before shutting down. We will provide migration support for paying customers moving to Cloudflare Workers. [Deno's JSR package registry for JavaScript and TypeScript] will continue operating, with its infrastructure moving to Cloudflare. Forbes argues that this acquisition of Deno "turns a long-standing objection to Cloudflare Workers, the claim that applications built on it cannot easily leave, into a selling point." For CIOs evaluating serverless and edge platforms, portability now has a concrete answer... Released in August, [celld] is a single Rust binary that runs Workers and Durable Objects across many machines, with object storage as its only external dependency. Operators run multiple celld instances against one storage bucket, and the software handles placement, routing and persistence. Dahl and Belder will now lead an effort to merge celld into workerd and make self-hosting a supported way to run Workers applications. With this, customers can build an application on Cloudflare's network and move it to a private data center without rewriting it. "With Deno, we improved the experience of writing JavaScript," Dahl argues on the Cloudflare blog, "but we didn't fundamentally change what developers had to assemble around the runtime. The bigger problems are around networked applications: distributing computation, coordinating state, data storage in general, and autoscaling to meet demand..." Could the programming model make partitioning across machines part of the design from the start? The solution clicked into focus when I read about Cloudflare's Durable Objects. It provided a very powerful abstraction: the distributed singleton with a SQLite database. Each Durable Object is like a small, individually addressable server with its own relational database. Its JavaScript execution is single-threaded (which is easy to reason about), it handles WebSockets, and its local SQLite database can be accessed synchronously. By building a chat application using one Durable Object per channel, you have sharded your data and WebSocket connections, and thus made your application scalable... What excites me is the leverage this model gives developers: compute, relational databases, queues, and real-time communication primitives designed for applications distributed across machines. Now Dahl and 12 of his Deno colleagues "will work to build out Cloudflare's Workers platform," explains The Register, "expanding it for potential open-source use. He feels this approach is the way to go." "Right now, every other server is really operating at the Linux VM layer. That is not what Cloudflare Workers are," he said... The ever-fickle Dahl first debuted Deno in 2018 as a rewrite of Node. The name 'Deno' is an anagram of Node, and it was Dahl's attempt to fix everything he felt he got wrong with Node — built-in fetch, a permission model, native TypeScript support et al. Sequoia backed Dahl's company for $21 million in 2022, and as of August, Deno amassed 400,000 monthly users. Nonetheless, Node's gravity proved too heavy for Deno to achieve escape velocity. "What we found over years of working on Deno is that you can't really deviate from Node.js very much," Dahl told The Register. "As we continued to try to get adoption for Deno, we found we had to essentially backpedal on some of the original promises and become more Node compatible over time, and that left us as a kind of an alternative Node.js implementation." Going forward, Cloudflare will supply Deno with bug fixes and security patches for the next year, while Dahl looks for a new home for the MIT-licensed open source project. Dahl's worked could bring "yet another revolutionary turn for server-side JavaScript," the article argues, "offering a runtime that would require only 300 KB of memory per instance, rather than the hundreds of megabytes now required for Node/Deno. Such savings could quickly add up for a cloud provider, especially one serving the voracious agentic market." And as Dahl wrote on the Deno blog, "The need for better abstractions is especially acute with AI. Durable Objects bring together capabilities that are particularly useful for agent harnesses: inexpensive, serverless execution, persistent state, WebSockets, and a high-level JavaScript interface. This is what I'm most excited to explore and why celld focuses on Durable Objects."

Read more of this story at Slashdot.
to be limited to / to be confined to (HSK 7-9)
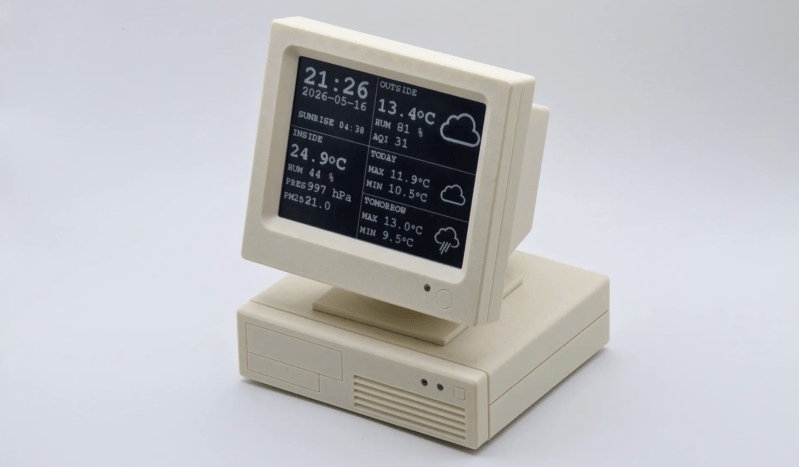
Modern computers are towers of glass and metal with very few large deviations from one to another. Monitor A will go against B, except you can’t tell them apart unless …read more
Millions of current and former students at California's public school have had their data stolen — including names, date of birth, and addresses — stolen in a breach, reports the Los Angeles Times. The breach affects students "who took the state's mandated standardized tests that annually assess their academic proficiency, education officials announced Friday." The compromised information affects many more than the state's current 5.7 million public-school students as the breach dates back to 2023 enrollments. Students who left California but did not confirm their transfer to another school also were affected, dating back to 2006. The data breach involved [nonprofit] Educational Testing Service or ETS, which provides extensive services to California [including test participation and assessment data]... Affected former students, including those who are now adults, are eligible for 24 months of free identity-protection services and identity-restoration help if there is identity theft. Officials said that parents and guardians may want to consider requesting a free credit freeze for their children who are under 16 to help prevent unauthorized accounts from being opened in the names of their children. The breach involved a compromised login credential, according to a web page about the incident from California's Department of Education. The compromised credential was then used to copy files with student information at "various" times between May 22 and September 18, 2026, which drew concern from a cybersecurity expert interviewed by the Los Angeles Times: "A stolen login credential should not become a months-long passport to millions of students' personal records," said Anton Dahbura, executive director of the Johns Hopkins University Information Security Institute. "If that is what happened here, the critical question is why authentication safeguards, access restrictions, and monitoring systems failed to detect and stop the unauthorized activity." He added: "Incidents like this expose a fundamental weakness in how we manage student data: School systems may outsource the storage and processing of sensitive information, but they cannot outsource the consequences of a breach. When millions of student records are concentrated with a single vendor, one security failure can become a statewide problem with consequences that follow children for years." A spokesperson for ETS told the Times that they've now implemented additional safeguards, including strengthened access controls, enhanced monitoring, and more third-party review of their security practices.

Read more of this story at Slashdot.